When Nobody Owns the Data Problem
Two business units report different revenue figures. The data team traces the discrepancy to conflicting definitions. Compliance asks who approved access to a sensitive dataset, but nobody can provide a complete audit trail.
The organization has invested in data platforms and analytics. Yet, it struggles to agree on which data to trust and who is accountable when something goes wrong.
This is a data governance problem.
As data spreads across business applications, cloud platforms and AI systems, informal practices become harder to manage. Policies may exist, but their effectiveness depends on whether ownership is clear, controls are enforced and exceptions are resolved.
A data governance maturity model helps organizations evaluate these capabilities, identify gaps and prioritize improvements. The goal isn’t to achieve the highest score. It’s to ensure that data is governed consistently, risks are controlled and business teams can use information with confidence.
Whether your organization is establishing its first data governance practices or refining an existing program, a data governance maturity model helps identify gaps and prioritize improvements. It can also help organizations using Master Data Management (MDM) tools assess how well governance policies, ownership, data quality, and accountability are established.
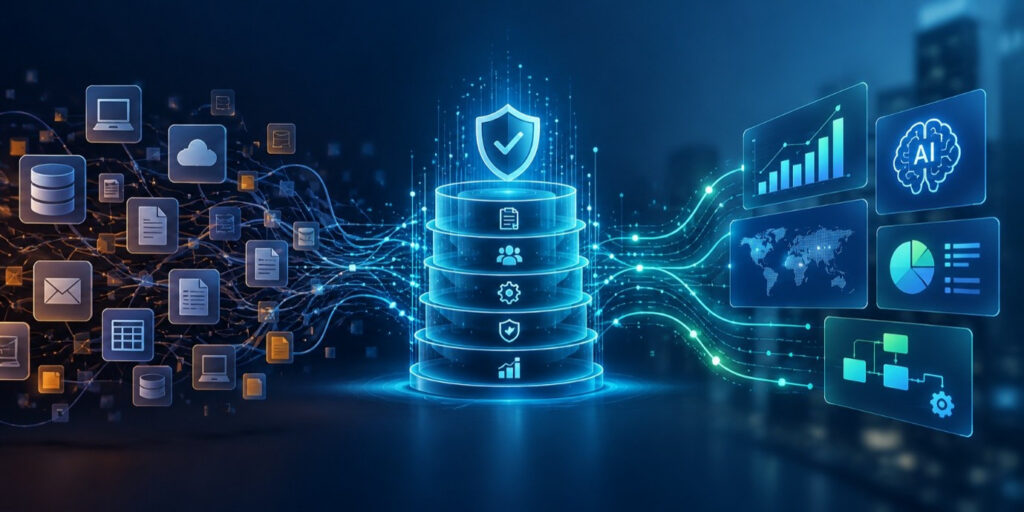
What Is a Data Governance Maturity Model?
A data governance maturity model evaluates how effectively an organization defines, implements, monitors and improves its data governance practices.
It focuses on the rules, responsibilities and controls that determine how data is owned, accessed, protected, maintained and used.
A practical model assesses five questions:
- Ownership: Are responsibilities and decision rights clearly defined?
- Consistency: Are policies and standards followed across business units?
- Control: Are access, privacy and quality requirements enforced?
- Evidence: Can the organization demonstrate that governance works?
- Improvement: Are governance outcomes measured and acted upon?
This is different from assessing overall data maturity. The focus here is exclusively on governance effectiveness, not the maturity of an organization’s analytics, infrastructure or data capabilities in general.
The Five Levels of a Data Governance Maturity Model
The following five-level framework is a practical model for enterprise self-assessment, rather than a claim that one maturity scale is universally standardized.
| Level | Characteristics | Priority |
|---|---|---|
| 1. Ad hoc | Ownership is unclear, policies are informal and issues are resolved reactively. | Assign owners and document essential policies. |
| 2.Developing | Basic policies and roles exist, but adoption varies across teams. | Standardize responsibilities and controls. |
| 3. Defined | Governance standards, stewardship roles and decision-making processes are documented. | Improve adoption and measure effectiveness. |
| 4. Managed | Controls are monitored, exceptions tracked and governance KPIs reviewed. | Strengthen preventive controls and automation. |
| 5. Adaptive | Evidence and monitoring drive continuous improvement as business needs and risks change. | Sustain effectiveness and adapt to emerging risks. |
What separates one level of Data Governance Maturity from another?
The difference isn’t the number of policies, committees or governance tools an organization has. It’s whether governance is consistently applied, evidenced and improved.
For example, a company may have named data owners but still operate at Level 2 if those owners lack authority and unresolved issues have no clear escalation path. Another organization with fewer tools may demonstrate stronger maturity because responsibilities are understood and controls work reliably.
Maturity should reflect actual operating behavior, not documented intent.
“Organizations must move beyond traditional data governance to build AI-ready enterprises, turning trusted data into a catalyst for autonomous decision-making, faster innovation, and measurable business impact.”
Krishna Kumar Chikkirala,
Vice President –AI & Data, Everforth Quinnox
Seven Dimensions to Include in a Data Governance Maturity Assessment
A useful data governance maturity assessment evaluates distinct capabilities before combining them into an overall score.
| Dimension | What to assess |
|---|---|
| 1. Governance and oversight | Executive sponsorship, decision rights and escalation |
| 2. Ownership and stewardship | Accountable owners and active data stewards |
| 3. Policies and standards | Policy coverage, adoption and exception handling |
| 4. Data quality governance | Quality rules, issue ownership and remediation |
| 5.Metadata and lineage | Business definitions, traceability and impact analysis |
| 6.Privacy and compliance | Access reviews, sensitive-data controls and audit evidence |
| 7.Monitoring and improvement | Governance KPIs, corrective actions and review cadence |
Assessing these dimensions independently helps reveal weaknesses that an overall score might conceal. For instance, an organization could have strong privacy controls but poor ownership of critical business data.
Established approaches can also provide useful reference points. TDWI’s Data Governance Maturity Model Assessment uses approximately 75 questions across five categories and provides overall and dimension-level scores. See the TDWI assessment guide.
For executive oversight, ISO/IEC 38505-1:2026 provides principles for governing the effective, efficient and acceptable use of organizational data. A maturity assessment can complement such guidance by evaluating how governance operates in practice.
Synthetic data can help organizations test data quality, validate governance controls, and support AI development while reducing reliance on sensitive production data. However, synthetic datasets still need to be assessed for privacy risks, bias, and fitness for purpose.
Explore further: Download The Synthetic Data Master Guide to learn how to adopt synthetic data responsibly and at scale.
Data Governance Metrics That Matter
Maturity scores describe the state of governance capabilities. Data governance metrics show whether those capabilities are working.
Start with a small set of measurable indicators:
| Metric | Calculation | What it reveals |
|---|---|---|
| Ownership coverage | Critical assets with assigned owners ÷ total critical assets × 100 | Accountability |
| Policy compliance | Checks passed ÷ checks performed × 100 | Policy adherence |
| Quality-rule compliance | Valid records or checks ÷ total evaluated × 100 | Quality against defined rules |
| Issue resolution time | Median time from issue logging to verified closure | Remediation effectiveness |
| Access review completion | Reviews completed on time ÷ reviews due × 100 | Access governance |
Targets should reflect the organization’s baseline, risk appetite and regulatory obligations. Critical exceptions should be reported separately so that a high average doesn’t hide a serious control failure.
Consider a company with 95% ownership coverage but recurring data disputes. The percentage alone suggests progress, but the disputes may indicate that ownership is nominal rather than effective. Metrics become valuable when leaders investigate what the numbers reveal and assign corrective action.
The business case for data governance is becoming more urgent as organizations scale AI. Gartner predicts that by 2027, 60% of organizations that fail to address cultural challenges in data and analytics governance will fail to govern AI successfully. The finding highlights why governance requires more than policies and technology. Clear ownership, accountability and consistent adoption across teams are essential to making governance work in practice. Source: Gartner, September 2026.
How to Conduct a Data Governance Maturity Assessment
A useful assessment should result in a prioritized improvement plan, not just a score.
1. Define the scope. Identify critical data domains, business units and regulatory requirements. Start where governance failures could have the greatest impact.
2. Gather evidence. Review ownership registers, policies, access reviews, quality reports, lineage documentation and audit findings. Validate documentation through interviews and sample testing.
3. Score each dimension. Use the five-level rubric consistently. Score demonstrated practices, not planned initiatives or policies that aren’t followed.
4. Identify critical gaps. Prioritize findings by business impact, regulatory exposure, recurrence and remediation effort.
5. Assign owners and targets. Give every priority action an accountable owner, deadline, baseline and measurable outcome.
6.Reassess periodically. Track progress and repeat the assessment after significant changes to business processes, regulations, platforms or data usage.
Example: Turning a score into action
Suppose a financial services organization scores 4 out of 5 on privacy controls but only 2 on data ownership and quality governance.
Rather than investing equally across every dimension, it should first assign owners to critical data domains, establish quality thresholds and introduce issue-resolution targets. Existing privacy controls can be maintained while weaker capabilities improve.
The assessment is useful when a low score leads to a specific intervention and a measurable result.
Common Mistakes That Limit Governance Maturity
Treating governance as an IT-only responsibility. Technology teams can implement controls, but business owners must define data meaning, quality expectations and acceptable use.
Measuring activity instead of effectiveness. Policies published and meetings held are not proof that controls work. Measure adherence, exceptions and verified remediation.
Automating unclear processes. Tools can enforce rules, but they cannot compensate for ambiguous decision rights or inconsistent definitions. Standardize the process before automating it.
Treating assessment as a one-time exercise. Governance needs change as regulations, systems and data usage evolve. Review performance regularly and reassess when material changes occur.
From Governance Policies to Measurable Outcomes
Improving governance maturity can strengthen accountability, support audit readiness, reduce recurring data disputes and provide a stronger foundation for responsible AI adoption.
Everforth Quinnox’s Data Services capabilities provide relevant context for organizations looking to connect governance requirements with their data environments and operational processes. The essential principle is that governance must work across business teams and technology systems, rather than exist only as a policy framework.
Leaders should connect three elements:
1. Clear governance operating model
2. Measurable controls
3. A continuous improvement process
Assess Your Data Governance Maturity
Where does your organization stand today? Are data owners accountable, are policies consistently enforced, and can you demonstrate that governance controls work?
Take the Data Governance Maturity Assessment to evaluate seven governance dimensions, identify areas that need attention and receive suggested next steps.
The assessment provides an indicative self-assessment, not a certification or audit opinion. Use the results to identify priorities and decide where deeper evaluation is needed.
As data ecosystems become more distributed and AI adoption expands, governance will increasingly be judged by its effectiveness, not its documentation.
The leadership question is no longer whether a governance framework exists. It’s whether the organization can demonstrate that it works.
Head – Digital Marketing, Everforth Quinnox
FAQs
A data governance maturity model is a framework that helps organizations assess how effectively they manage, protect, maintain, and use their data. It evaluates capabilities such as data quality, ownership, security, compliance, and accountability to identify gaps and define a roadmap for improvement.
Data governance maturity is assessed by evaluating key areas such as data quality, ownership, policies, security, compliance, and accountability against defined maturity levels. Organizations score each area based on existing processes, controls, and practices, identify capability gaps, and use the results to prioritize improvements and build a roadmap toward AI-ready data governance.
Use Everforth Quinnox’s Data Governance Maturity Assessment Tool to evaluate your current practices and identify opportunities to strengthen your data governance capabilities.
Organizations can improve data governance maturity by establishing clear data ownership, standardizing governance policies, improving data quality, strengthening security and compliance controls, and implementing continuous monitoring. Regular maturity assessments help identify gaps, prioritize improvements, and build a roadmap toward trusted, AI-ready data.
Common challenges include fragmented data across systems, unclear data ownership, inconsistent data quality, siloed teams, limited executive support, and difficulty enforcing governance policies. Legacy systems and evolving regulatory requirements can further complicate efforts.
Organizations should conduct a formal data governance maturity assessment annually and review progress quarterly. Additional assessments are useful after major technology changes, regulatory updates, mergers, or AI initiatives to ensure governance capabilities keep pace with business needs.